
How integration groups work
An integration group is a set of integrations that share a tag. Select a tag key, and each of its values becomes a group. For example, the keyDivision collects integrations tagged Division=payments into the group Division:payments.
Group membership is derived from each integration’s tags: its AWS account tags, and any tags defined in Plerion, which replace the AWS account tag with the same key.
- Plerion reads account tags when your management account or delegated administrator integration is scanned, and updates group membership automatically.
- Saving tags defined in Plerion updates the groups that use those keys within a few seconds.
- Newly onboarded integrations join their groups shortly after registration.
- Plerion recalculates every group at least once a day.
- Matching is case-sensitive:
BusinessUnit:devandBusinessUnit:Devare different groups.
Groups are built from the tags on AWS accounts in AWS Organizations and from tags defined in Plerion, not from tags on resources.
Prerequisites
- An integration that can read your AWS organization: your management account, or a member account granted read access by a delegation policy. See Delegate AWS Organizations read access to a member account. If you cannot tag your AWS accounts, define tags in Plerion instead.
- The Organization Admin role, to configure integration groups.
Steps to select tag keys
1
Go to Settings > Integration groups
The page lists the tag keys collected from your AWS accounts and the groups your current selection produces.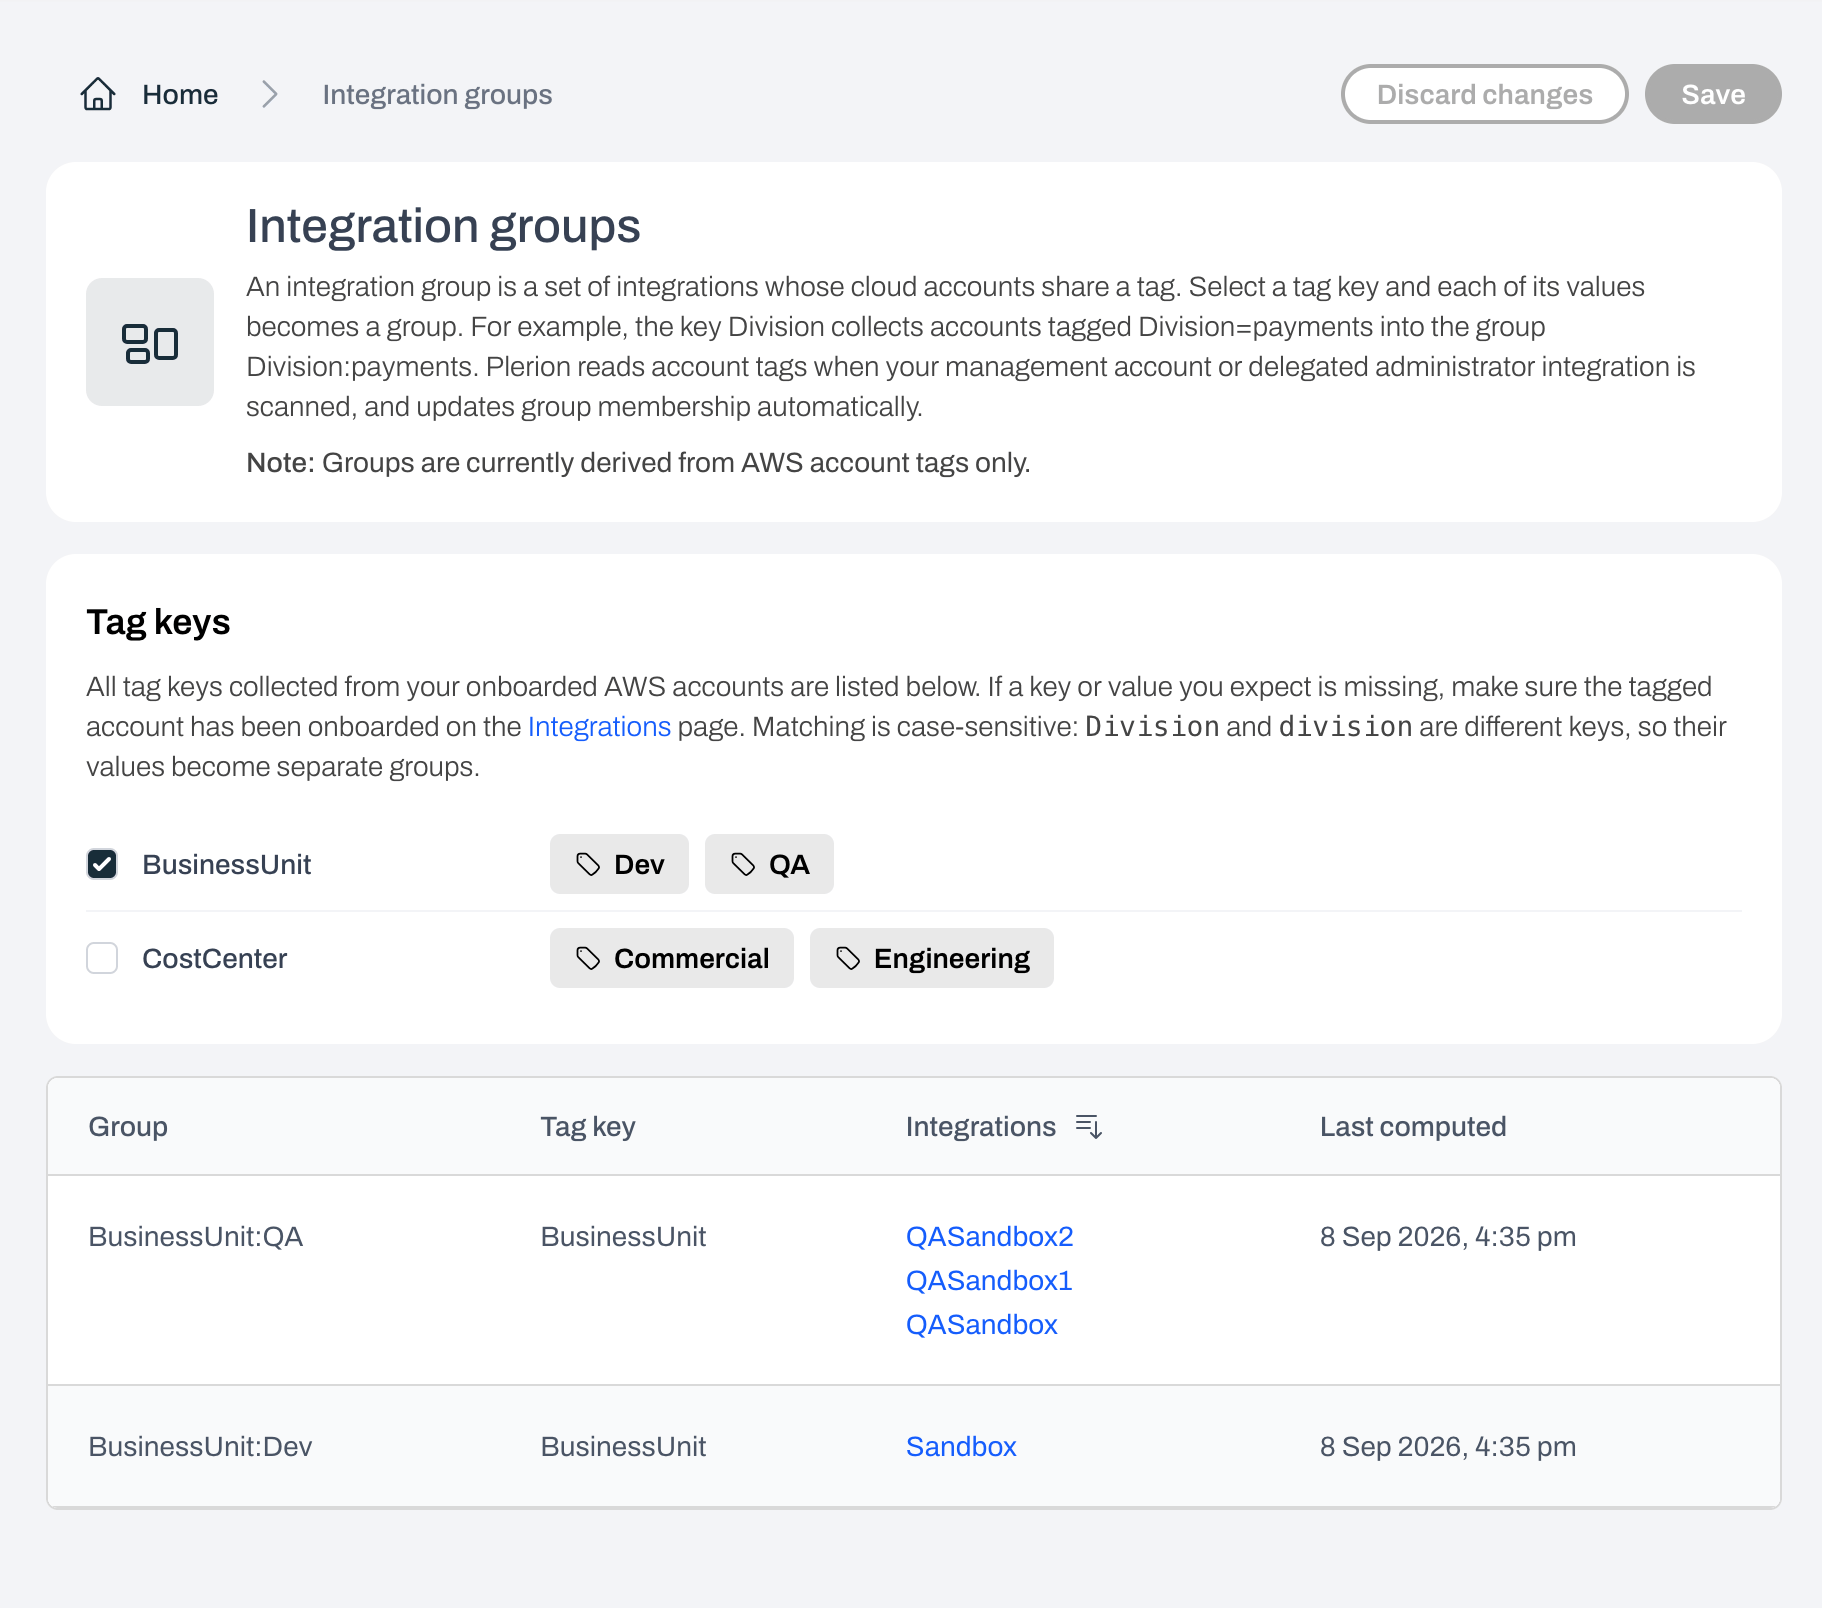
2
Select tag keys
The Tag keys card lists every tag key found on your integrations, from AWS accounts and from tags defined in Plerion, with the values found for each key. Check each key you want to group by, and each of its values becomes a group. You can select up to 20 keys.If a key or value you expect is missing, make sure the tagged account has been onboarded on the Integrations page.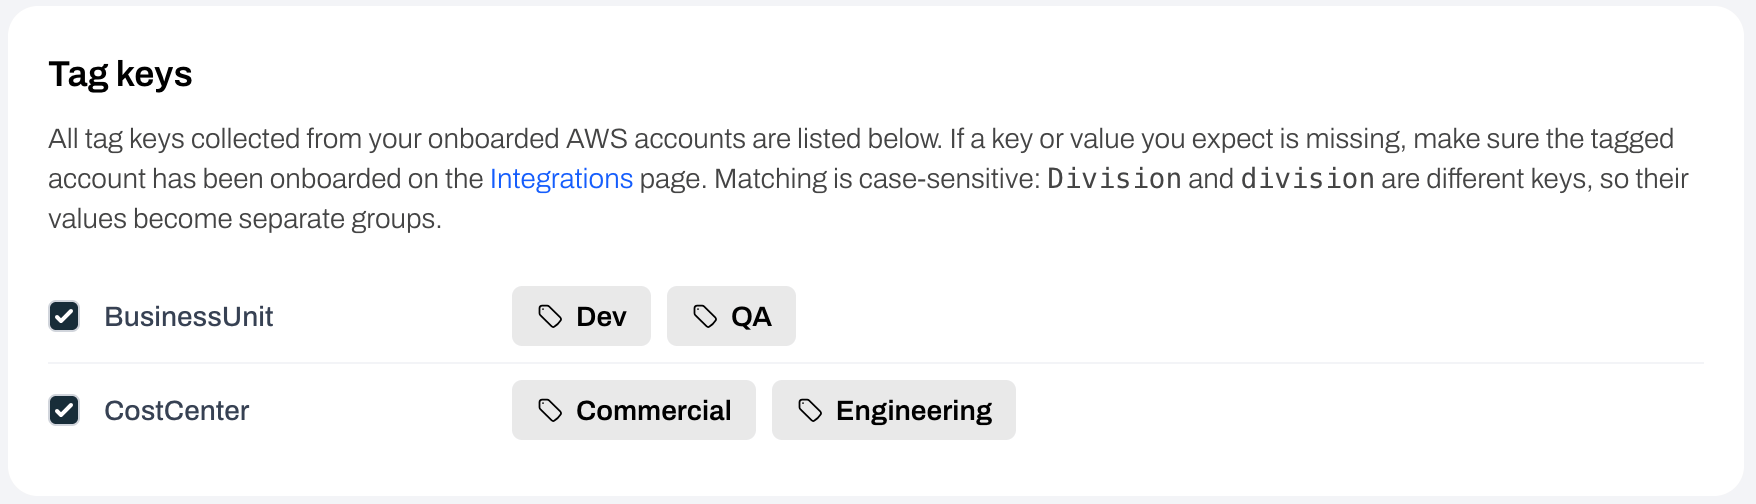
3
Click Save
While you have unsaved edits, the page shows an Unsaved changes chip, and Discard changes returns to the saved selection. On save, Plerion confirms with Tag keys saved. Groups are updating now. The groups table refreshes within a few seconds as the recalculation completes.
Define tags on an integration
Tag your AWS accounts in AWS Organizations where you can: Plerion reads those tags on every scan, so a newly tagged or re-tagged account moves between groups with no change in Plerion. When tagging the account is not an option, define tags on the integration in Plerion instead. Both kinds of tag feed the same groups.1
Open the integration's settings page
Go to Settings > Integrations and select the integration. The Tags section lists the tags defined in Plerion and the tags read from the cloud account.
2
Click Edit
Add a tag by typing a key and a value, or pick a key already used on another integration to keep your keys consistent. Keys and values are case-sensitive:
Env and env are different keys. An integration can carry up to 50 tags defined in Plerion.3
Click Save changes
Groups that use one of the changed keys recalculate within a few seconds.
Removing a tag key
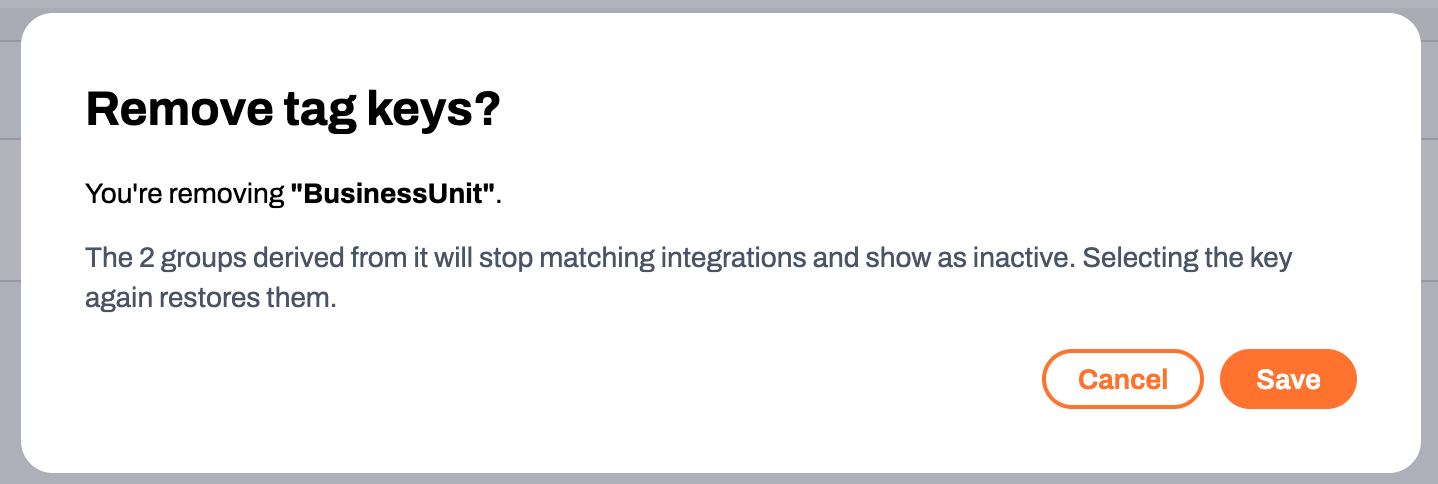
Deselecting a key and clickingSave opens the Remove tag keys? confirmation. The groups derived from that key stop matching integrations and show as Inactive. Reselecting the key restores them.
Filter by integration group
The Integration group filter narrows results to the integrations currently in the group. It is available on:- Findings, Assets, Vulnerabilities, and Alerts
- Top risks, Compliance, and Data security
- Findings, alerts, and vulnerability widgets in Custom dashboards
- Finding, asset, and vulnerability conditions in Workflows