> ## Documentation Index
> Fetch the complete documentation index at: https://docs.plerion.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Getting started with GCP workload scanning
> Turn on workload scanning for a GCP organization integration, run the access command, confirm the setup, and find your first results
With **[GCP workload scanning](/guides/integrations/gcp/workload-scanning/overview)**, you scan the workloads in a Google Cloud organization you've already connected to Plerion. There is no separate integration to create. You turn on the capability, fill in one extra wizard step, and re-run the access command with the flags Plerion adds for you.
Check the [prerequisites](/guides/integrations/gcp/workload-scanning/prerequisites) first, in particular the billing account and who holds **Billing Account User** on it.
If your organization is already connected, open its detail page, go to **Capabilities** and click `Edit`. The Capabilities panel has the same settings as steps 3 and 4 below. Save it, then run the access command from `Update Plerion access` as in step 5. If you're connecting the organization for the first time, follow the steps from the top.
***
## Steps to turn on workload scanning
On the Plerion dashboard, go to `Settings` > `Integrations`.
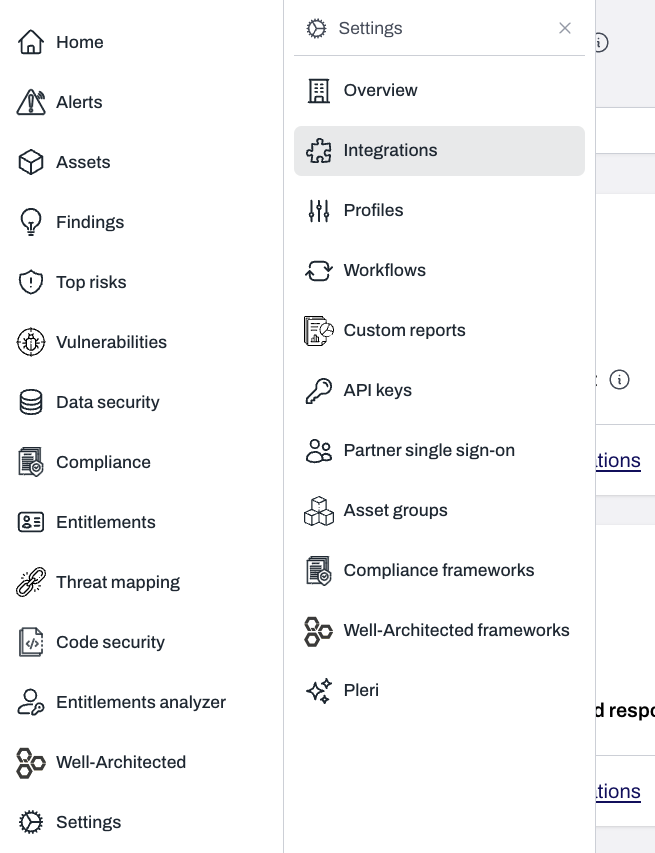 Open your existing GCP organization integration, or find **GCP**, click `+`, and choose **GCP organization** to start a new one. See [Steps to connect a GCP organization](/guides/integrations/gcp/overview#steps-to-connect-a-gcp-organization) for the base integration.
* **Misconfigurations and compliance** and **Identities and permissions** are always on.
* Turn on **Workload scanning**. The **Configure workload scanning** step appears.
* Click `Next`.
* **Workload scan types**: **Vulnerabilities** and **Software bill of materials (SBOM)** are on by default. Turn on **Sensitive data** to report secrets found on disks, in images, and in source.
* **Workloads**: **Compute Engine instances**, **Compute Engine managed instance groups**, **Compute Engine custom images**, **Cloud Run services**, **Cloud Functions (2nd gen)**, and **Cloud Functions (1st gen)** are all on for a new integration. Turn off any you don't want scanned. Each type is independent. See [Coverage](/guides/integrations/gcp/workload-scanning/coverage) for what each one covers.
* **Billing account ID**: required. Enter the billing account the scanning project will be linked to, in the form `012345-6789AB-CDEF01`. The field links to the [Google Cloud billing console](https://console.cloud.google.com/billing) and shows the `gcloud billing accounts list` command.
* **Networking**: choose how scanner VMs reach the internet.
* **Ephemeral external IP** *(default)*: each scanner VM gets a temporary public IP for outbound traffic and releases it when the scan finishes. A firewall rule blocks all inbound traffic. No standing cost.
* **Cloud NAT**: required if your organization enforces `constraints/compute.vmExternalIpAccess`. Cloud NAT stays provisioned in each region you select below and is billed whether or not a scan is running.
* **Workload regions (optional)**: limit scanning to specific regions. Leave it empty to scan every region a workload is found in. With **Cloud NAT**, select at least one region. NAT is provisioned only in the regions listed here.
* Click `Next`.
Use the **Script** or **Terraform** tab. Plerion adds the workload scanning options to the command for you.
* Open [Google Cloud Shell](https://shell.cloud.google.com) as an Organization Admin who also holds **Billing Account User** on the billing account.
* Paste and run the generated command. It now includes `--enable-workload-scanning`, `--billing-account `, `--workload-types `, and, if set, `--workload-regions ` and `--nat`.
* Before creating anything, the script confirms it can read the billing account. In **Ephemeral external IP** mode, it also confirms the organization policy doesn't deny external IPs. Either failure stops the script with a message saying what to change.
* The script creates the scanning project, links billing, enables its APIs, and creates its network and scanner service accounts. It grants the roles in [Access and permissions](/guides/integrations/gcp/workload-scanning/access-and-permissions) to the **tenant service account**, the service account onboarding created for Plerion in your Plerion service project. Its last line is `Scanning project: `. Keep that ID.
* Copy the generated `terraform.tfvars` from the tab. It includes `enable_workload_scanning`, `billing_account_id`, `workload_types`, and, if set, `workload_regions` and `workload_nat`.
* Run `terraform init` and `terraform apply` with Application Default Credentials that belong to the same admin account.
* Terraform runs no prechecks. If billing or an organization policy blocks it, the apply fails at the affected resource.
Registration completes in the background. For a new integration, the wizard moves on to choosing projects once Plerion detects the organization. For an existing integration, you're done in Plerion.
On the integration's detail page, go to **Capabilities** > `Edit`. The **Scan project setup** checklist at the bottom of the panel shows **Verified** when every check passes, or **Needs attention** with the failing check and reason:
* Workload scanning configured
* Scanning project labeled
* Billing account linked
* Plerion scanning network present
* Scanner service account exists
* Tenant service account role bound
* Cloud Run API enabled (when Cloud Run services or Cloud Functions (2nd gen) is on)
* Source scanner service account exists (when Cloud Functions (1st gen) is on)
Click the refresh icon to run the checks again after fixing something. The checklist appears only once Plerion has registered the scanning project. If you ran the script a few minutes ago and it isn't there yet, check back shortly.
The integration's badge reads **Workload** in the integrations list and **CWPP** (Cloud Workload Protection Platform) on the detail page. Until the scanning project is registered, it carries the warning **Workload scanning setup is incomplete. Re-run the onboarding script.** Afterward it reads **Setup complete. Scans run after each posture scan.**
Workload scanning runs after each project's posture scan completes, so the first workload findings arrive within one scan interval, up to 24 hours on the default daily schedule. To start sooner, open a project under the organization and click `Scan now`. That runs a posture scan of the project, and the workload scan follows it.
Open a project under the organization integration. With workload scanning on, its page has three tabs:
* **Scans**: every scan of the project, posture and workload.
* **Workload scans**: each workload scan run with its status (**in progress**, **completed**, **failed**, or **timed out**), the assets covered, timings, and a message for any asset that couldn't be scanned.
* **Scanners**: the scanner VMs and jobs Plerion ran for the project.
Vulnerability, SBOM, and secrets findings appear against the scanned asset in Plerion's findings views.
***
## Next steps
* [How scanning works](/guides/integrations/gcp/workload-scanning/how-scanning-works)
* [Coverage](/guides/integrations/gcp/workload-scanning/coverage)
* [Managing workload scanning](/guides/integrations/gcp/workload-scanning/managing-workload-scanning)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.